Agentic AI Security in 2026: Risks, Attacks and Best Practices
From prompt injection to unauthorized actions, discover how organizations can secure AI agents before autonomy becomes a security liability.
Artificial intelligence is moving beyond answering questions. Today, AI agents can retrieve sensitive documents, interact with enterprise applications, query databases, execute workflows, and take actions on behalf of users. This shift is creating new opportunities for automation—but it is also expanding the cybersecurity attack surface.
Unlike a traditional chatbot, an AI agent may have access to tools, persistent memory, APIs, and business systems. If an attacker manipulates the agent or exploits weaknesses in its integrations, the consequences can extend beyond an inaccurate response to unauthorized data access, unintended transactions, or potentially dangerous system operations.
Microsoft’s security research published in 2026 has highlighted how attacks against AI agent frameworks and tool integrations can turn prompt injection into an execution risk. Meanwhile, the OWASP GenAI Security Project continues to develop practical guidance for addressing vulnerabilities in AI-powered applications.
For security leaders, the question is no longer simply whether an AI model produces safe answers. It is whether the entire system can be trusted to act securely.
1. What Makes Agentic AI Different?
Traditional AI assistants primarily generate responses based on user prompts and available context. Agentic AI systems can go further by planning tasks, selecting tools, processing results, and executing multiple steps with varying degrees of autonomy. Consider an AI agent designed to help an IT team investigate security incidents. It might retrieve logs, query a threat intelligence platform, inspect user activity, and prepare an incident report. If granted additional permissions, it might also disable accounts or modify security configurations. These capabilities introduce a critical distinction: an AI agent can translate manipulated information into real-world actions when its tools and permissions are not adequately controlled.
The security risk depends on the agent’s design, available privileges, connected systems, and level of autonomy—not simply on the underlying AI model.
2. Five Major Security Risks Facing AI Agents
Prompt Injection and Malicious Instructions
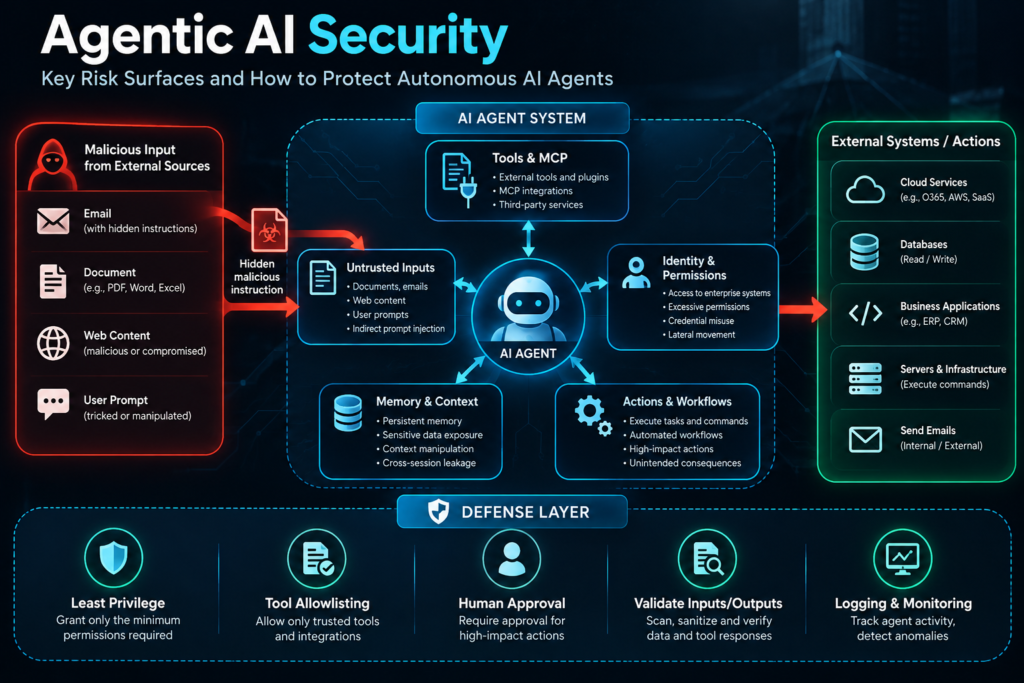
Prompt injection occurs when an attacker manipulates an AI system through instructions designed to override or influence its intended behavior. These instructions may appear directly in a user prompt or indirectly inside an email, document, website, or other content the agent processes. For example, an employee asks an AI agent to summarize a document. Hidden instructions within that document attempt to persuade the agent to retrieve confidential files and transmit their contents elsewhere. If the agent has excessive access and insufficient safeguards, the malicious instructions could influence its subsequent actions.
The challenge is that legitimate business content and malicious instructions may appear together. Treating all retrieved content as trustworthy creates opportunities for exploitation.
Excessive Permissions and Unauthorized Actions
AI agents often need access to enterprise tools to complete their tasks. However, granting broad permissions for convenience can create serious security weaknesses. An agent intended to read customer records might also have permission to modify them. An agent designed to analyze source code might be able to execute commands or access deployment credentials. If the agent is manipulated, compromised, or makes an incorrect decision, excessive privileges can increase the potential impact.
Organizations should apply least-privilege access, separate read and write permissions, and enforce authorization at the application and API layers rather than relying on the AI model to decide what it is allowed to do.
Model Context Protocol (MCP) and Tool Integration Risks
The Model Context Protocol (MCP) provides a standardized way for AI applications to connect with external tools and data sources. It can simplify integrations, but it also introduces security considerations around tool discovery, authentication, permissions, and the trustworthiness of connected services. A malicious or compromised tool integration could provide misleading instructions, return manipulated data, or request access beyond what the task requires. Security teams should verify tool provenance, authenticate connections, restrict available functions, validate tool inputs and outputs, and monitor activity across agent-to-tool interactions.
Memory and Context Poisoning
Some AI agents retain information across interactions or use shared context to complete longer-running tasks. If untrusted or manipulated information enters that memory, it may influence future decisions. For example, an agent could retain a misleading instruction from an earlier interaction and apply it during a later task involving sensitive business data. Organizations should establish clear memory-retention policies, distinguish trusted information from untrusted content, restrict access to stored context, and provide mechanisms to inspect, correct, and remove compromised information.
Data Leakage and Weak Monitoring
An AI agent with access to emails, customer records, source code, or internal knowledge bases can become a pathway for sensitive information exposure. The risk increases when agents can move information between systems without adequate controls or when security monitoring cannot distinguish legitimate automation from suspicious activity. Traditional identity and endpoint controls remain important, but organizations must also understand what the agent accessed, which tools it invoked, whose permissions it used, and what actions followed.
3. How an AI Agent Attack Can Unfold
Consider a hypothetical enterprise scenario involving an AI agent connected to email, a document repository, and a business application.
Stage 1 — Initial exposure: The agent processes an external document containing malicious instructions.
Stage 2 — Manipulation: The instructions influence the agent’s reasoning or tool selection.
Stage 3 — Unauthorized access: The agent attempts to retrieve information using permissions that are broader than necessary.
Stage 4 — Harmful action: If additional controls are absent, the agent may attempt to share information or modify business records.
Stage 5 — Detection and response: Effective monitoring can identify unusual tool calls, unexpected data access, or actions outside the agent’s normal operating pattern.
This scenario illustrates why prompt security alone is insufficient. An organization must secure the complete execution path, from incoming content and identity permissions to downstream tools and resulting actions.
4. A Practical Framework for Securing AI Agents
Organizations can reduce these risks through a layered security approach.
Enforce least privilege. Give every agent only the identities, data access, and tools necessary for its defined purpose. Separate read-only operations from actions that change business systems.
Validate every tool call. Apply authorization and policy checks outside the AI model. Validate parameters, restrict commands, and block requests that violate established business rules.
Require human approval for high-impact actions. Actions such as transferring funds, deleting records, changing security controls, or sending sensitive information externally should require appropriate authorization.
Treat external content as untrusted. Apply safeguards to documents, emails, websites, tool responses, and retrieved context. Prompt instructions should never replace conventional access controls.
Monitor agent behavior continuously. Log agent identity, user context, tool invocations, data access, policy decisions, and consequential actions. Alert on unusual activity and establish procedures to revoke credentials or suspend an agent when necessary.
Test the complete system. Assess the AI model, orchestration framework, integrations, APIs, identities, and connected infrastructure. Include adversarial testing for prompt injection, privilege escalation, data leakage, and unintended actions.
Security should be built into the agent lifecycle—from design and development to deployment, monitoring, and retirement.
5. What Security Teams Should Do Next
Before deploying autonomous AI agents across critical business workflows, organizations should maintain an inventory of agents and their integrations, identify sensitive data they can access, map their permissions, and determine which actions require human authorization. Security assessments should then test realistic attack scenarios, including indirect prompt injection, malicious tool responses, compromised integrations, and attempts to exceed authorized permissions. Findings should be prioritized according to business impact and addressed through technical controls, governance, and continuous validation.
The objective is not to eliminate AI-driven automation. It is to ensure that autonomy operates within clearly defined and independently enforced security boundaries.
Conclusion: Secure the Actions, Not Just the Model
Agentic AI introduces a fundamental shift in enterprise security. AI systems are no longer limited to producing information; they can interact with the applications, data, and infrastructure that keep businesses running. As adoption grows, organizations must extend their security strategies beyond model-level safeguards to include identity governance, tool security, authorization, data protection, monitoring, and adversarial testing. The central principle is simple: an AI agent should never receive more authority than its task requires, and no consequential action should depend solely on the model’s judgment.
At Clear Infosec, organizations can strengthen their security posture through structured security assessments, penetration testing, Red Teaming, security advisory, and continuous monitoring. As AI adoption accelerates, validating the security of AI-enabled workflows will become an increasingly important part of enterprise risk management.
Is your organization ready to secure its AI agents? Start by assessing what they can access, what they can execute, and how quickly your security team can detect and contain an unsafe action.